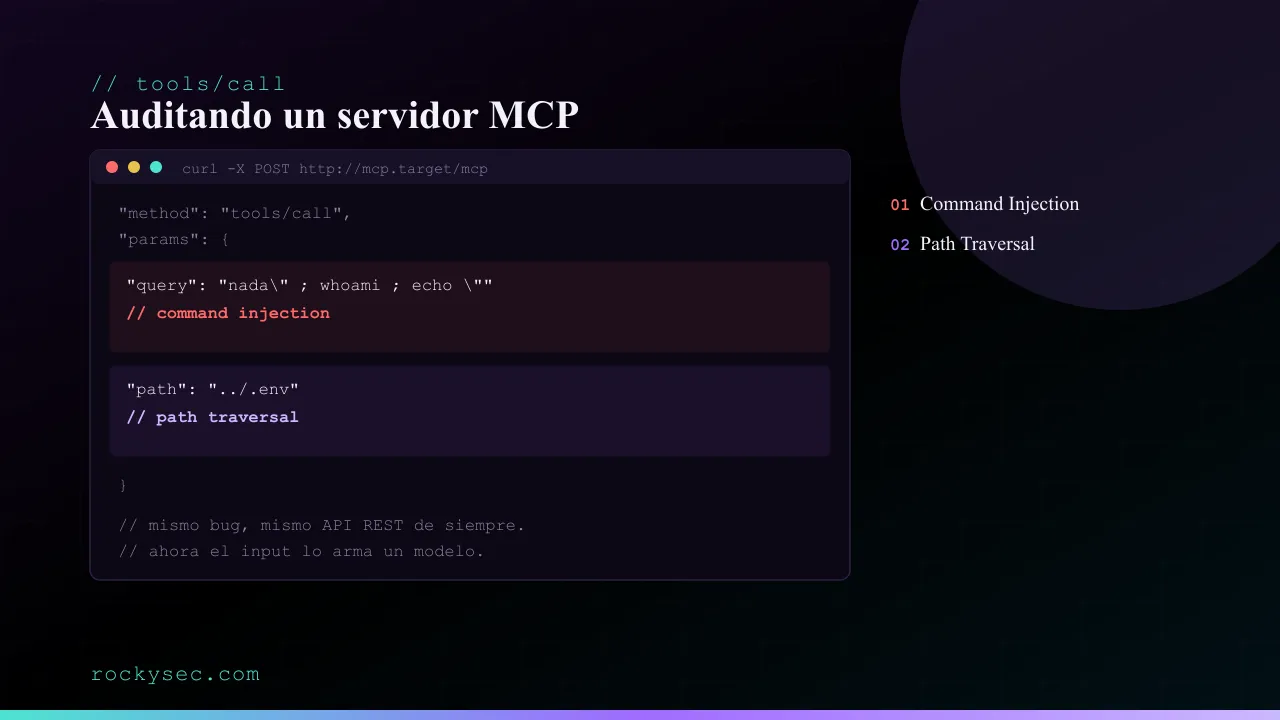
Auditing an MCP server: 2 flaws that keep showing up in production
Command injection and path traversal in remote MCP servers: the vulnerable file and line, a curl PoC for each one, and the fix, with your own lab to practice safely.
archive
Research, writeups and tutorials on offensive security, bug bounty and artificial intelligence.
Command injection and path traversal in remote MCP servers: the vulnerable file and line, a curl PoC for each one, and the fix, with your own lab to practice safely.
AI applied to bug bounty is no longer futurism: it speeds up recon, prioritises findings and drafts reports. Real use cases, hard limits and concrete risks.
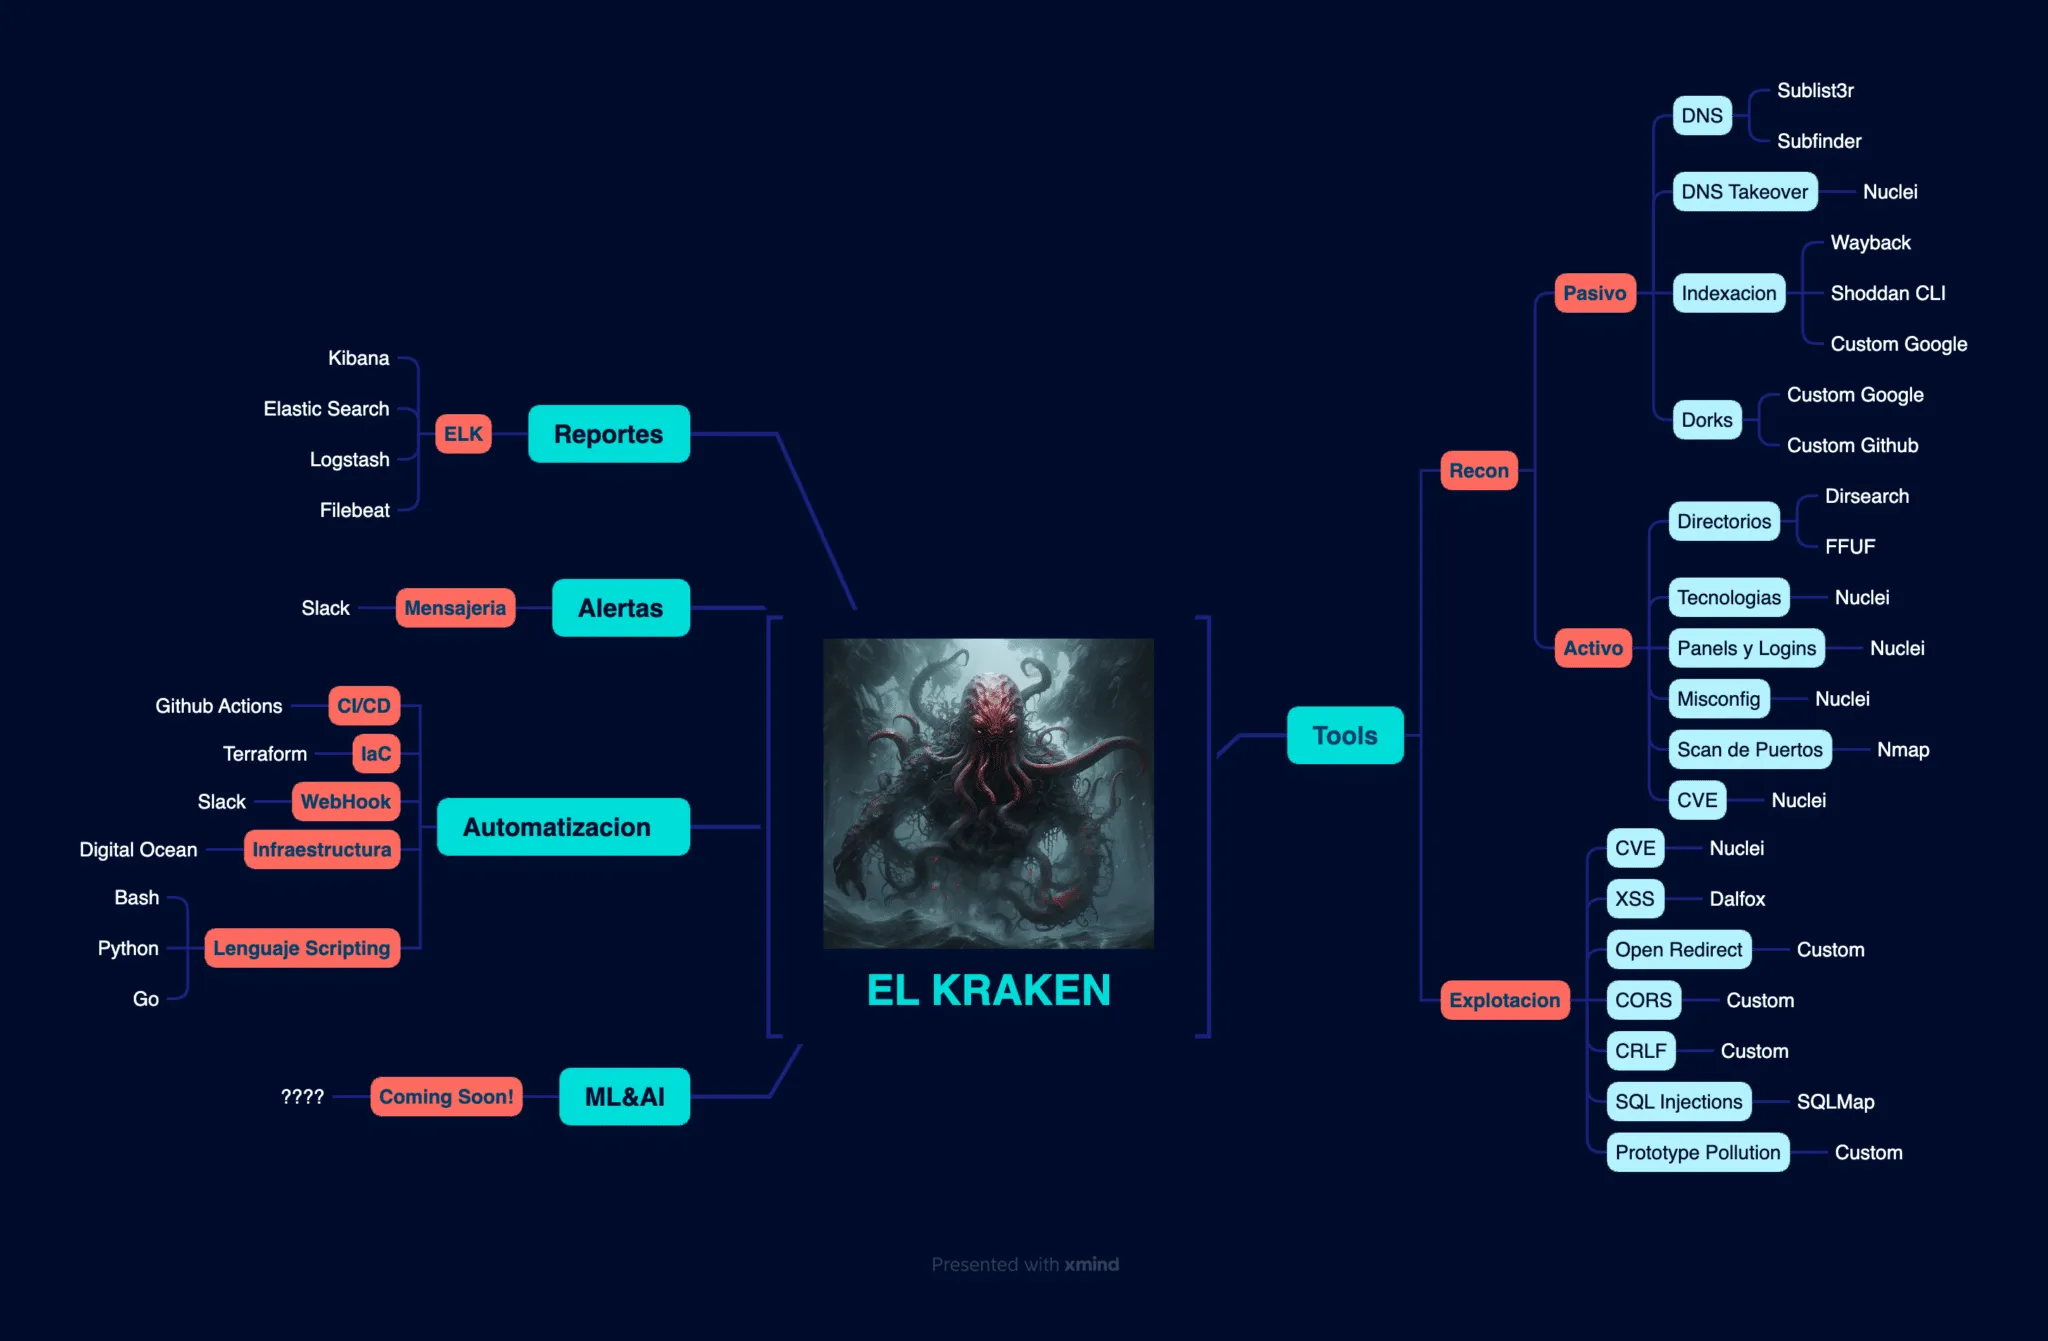
I presented El Kraken at Ekoparty 2023: an automated recon tool that speeds up bug bounty while cutting VPS costs using GitHub Actions and DigitalOcean.
How to spin up ephemeral scanning infrastructure with GitHub Actions and DigitalOcean, and ship the results to an ELK stack for real-time metrics and visibility.
El Kraken is a modular bash tool that automates recon and known-CVE exploitation end to end, chaining nuclei, subfinder, wayback and dirsearch together.
What an IDOR is, how it is exploited by changing an identifier in the URL, which tools detect it in Burp Suite or ZAP, and the four practices that prevent it.
A recap of Meet4Shell 2022 hosted by the Argentine Bug Bounty community: talks on Electron app bugs, secrets exposed in Postman, and why community matters.